


It is a truth universally acknowledged that a better job rarely comes looking for you. The SC-200 exam is one of the clearest routes to it, and CertkingdomPDF equips that route with 415 practice questions for the Microsoft Security Operations Analyst exam and a free demo to start.
Microsoft SC-200 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Mitigate threats using Microsoft 365 Defender | 25-30% | - Hunt threats in Microsoft 365 Defender
|
| Mitigate threats using Microsoft Defender for Endpoint | 25-30% | - Configure Microsoft Defender for Endpoint environment
|
| Mitigate threats using Microsoft Defender for Cloud Apps | 20-25% | - Investigate and respond to threats
|
| Mitigate threats using Microsoft Defender for Identity | 15-20% | - Investigate and respond to identity threats
|
Questions & Answers: The SC-200 Exam
Online proctored or in-person testing center Book the Microsoft Security Operations Analyst exam through these official channels:
Once booked, your CertkingdomPDF practice questions arrive by email within 1 minute, so preparation starts the same day.
The passing score for the Microsoft Security Operations Analyst exam is 700 (scale of 100-1000), and registration costs $165 USD. A retake means the same fee again — a sound reason to test your readiness with the CertkingdomPDF engines before committing to a date.
CertkingdomPDF refunds you in full if you take the Microsoft Security Operations Analyst exam within 60 days of purchase and do not pass. The policy does not apply if the exam is taken within 3 days of purchase, if the exam was never actually taken, or to free materials or expired orders, and the candidate name must match the payer name. Submit a scan of your enrollment slip and the official Score Report PDF within 2 days of the exam; claims are processed within 7 days. As an alternative, exchange for two free exam products of equal value while keeping your original update service. Delivery is by email within 1 minute — contact support if nothing arrives within 2 hours.
Microsoft recommends these training resources for the Microsoft Security Operations Analyst exam:
After the training, the 415 practice questions from CertkingdomPDF let you make full use of sporadic time — short sessions that steadily convert study into readiness.
The Microsoft Security Operations Analyst exam presents 40-60 with 120 minutes available. That pace is demanding — rehearse it in the timed mode of the CertkingdomPDF Desktop Test Engine until it feels familiar.
The official Microsoft Security Operations Analyst outline comprises 4 domains. The three largest are Mitigate threats using Microsoft Defender for Cloud Apps (20-25%), Mitigate threats using Microsoft 365 Defender (25-30%), and Mitigate threats using Microsoft Defender for Identity (15-20%). The full list appears in the topics section above, and the 415 practice questions at CertkingdomPDF cover all of them.
The SC-200 exam is a Microsoft certification exam built around the Microsoft Security Operations Analyst syllabus shown above. It feeds into these credential paths: Microsoft Certified: Security Operations Analyst Associate. Precisely because the exam is demanding, passing it earns real attention from employers in 2026. CertkingdomPDF prepares you with 415 practice questions in PDF, Desktop Test Engine, and Online Test Engine formats.
Microsoft recommends having experience with Microsoft 365 Defender workloads, security operations, and incident response. Knowledge of Azure Active Directory, basic networking, and scripting is beneficial but not mandatory. Requirements can change, so verify the latest on the official Microsoft exam page before scheduling.
The complete preparation toolkit: 415 practice questions for the Microsoft Security Operations Analyst exam in three formats — a printable, expert-prepared PDF with instant download; a Desktop Test Engine for Windows that simulates the real exam with two practice modes and works offline; and an Online Test Engine for any browser on Windows, Mac, Android, and iOS with test history and performance review. Included as well: a free demo, 365 days of free updates, a 50% renewal discount afterward, and unlimited computer installations — all from a platform refined through years of expert effort.
Microsoft Security Operations Analyst Sample Questions:
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: You add each account as a Sensitive account.
Does this meet the goal?
- A. Yes
- B. No
Correct Answer: A 🗳️
Explanation: Only visible for CertkingdomPDF members. You can sign-up / login (it's free).
Your on-premises network contains two Active Directory Domain Services (AD DS) domains named contoso.
com and fabrikam.com. Contoso.com contains a group named Group1. Fabrikam.com contains a group named Group2.
You have a Microsoft Sentinel workspace named WS1 that contains a scheduled query rule named Rule1.
Rule1 generates alerts in response to anomalous AD DS security events. Each alert creates an incident.
You need to implement an incident triage solution that meets the following requirements:
Security incidents from contoso.com must be assigned to Group1.
Security incidents from fabrikam.com must be assigned to Group2.
Administrative effort must be minimized.
What should you include in the solution?
- A. one automation rule assigned to Rule1
- B. a playbook that is triggered by the creation of an alert
- C. a playbook that is triggered by the creation of an incident
- D. two automation rules assigned to Rule1
Correct Answer: D 🗳️
Explanation: Only visible for CertkingdomPDF members. You can sign-up / login (it's free).
You have a Microsoft 365 subscription that uses Microsoft Defender for Endpoint Plan 2 and contains a Windows device named Device 1. You initiate a live response session on Device1 and launch an executable file named File1.exe in the background. You need to perform the following actions:
* Identify the command ID of File1 exe.
* lnteractwithFile1.exe.
Which live response command should you run for each action? To answer, select the appropriate options in the answer area.
NOTE Each correct selection is worth one point.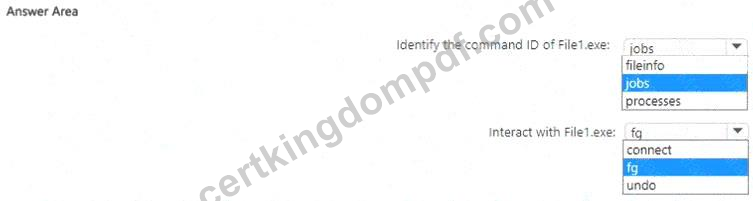
Correct Answer:

Explanation:
In Microsoft Defender for Endpoint (MDE) Live Response, security analysts can remotely connect to a device and execute forensic commands. When an executable is launched in the background during a live response session using the run command (for example, run File1.exe -background), the session creates a job associated with that command.
To identify the command ID of the background process, the correct command is jobs. The jobs command lists all currently running or completed background jobs initiated during the live response session. Each job entry includes details such as the job ID, command executed, and current status. This allows analysts to determine which process corresponds to File1.exe and its associated command ID.
Once the background process is identified, you can interact with File1.exe using the fg (foreground) command. The fg command is used to bring a background job to the foreground, allowing you to interact directly with it - for instance, to send inputs, observe outputs, or terminate it.
This procedure aligns with Microsoft Defender for Endpoint documentation, which specifies:
Use jobs to view or manage background jobs.
Use fg < JobID > to interact with a specific background process.
Therefore, the correct selections are:
Identify the command ID of File1.exe: jobs
Interact with File1.exe: fg
You have an Azure subscription that uses Azure Defender.
You plan to use Azure Security Center workflow automation to respond to Azure Defender threat alerts.
You need to create an Azure policy that will perform threat remediation automatically.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation: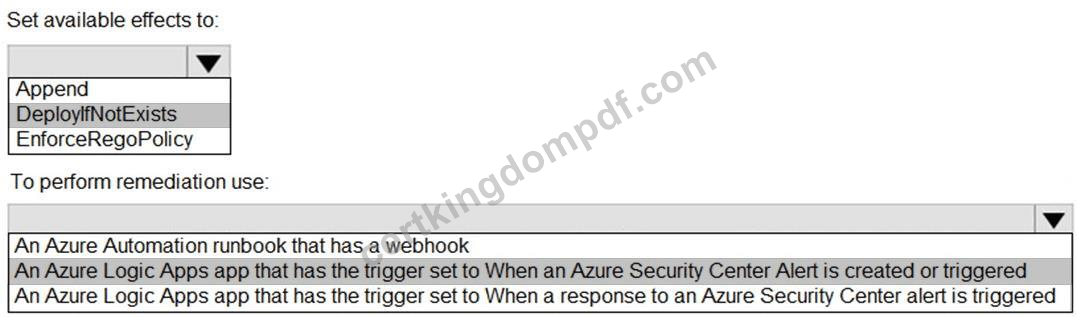
In Microsoft Defender for Cloud (formerly Azure Security Center), workflow automation allows you to automatically respond to security alerts and recommendations by triggering remediation actions.
When you create an Azure Policy to enforce automatic remediation based on Defender alerts or recommendations, the effect determines what the policy does when a resource is found noncompliant:
DeployIfNotExists is the correct effect to use for automatic remediation. This effect automatically deploys a remediation task (such as a Logic App or other automation) when a matching noncompliant resource is detected. It's commonly used in Defender for Cloud to deploy missing security configurations or initiate an automated remediation workflow.
Append only adds metadata or parameters to resources-it does not enforce or deploy remediation actions.
EnforceRegoPolicy is used for container compliance with Gatekeeper policies (Kubernetes), not for Defender workflows.
For the automation mechanism:
An Azure Logic Apps app with the trigger "When an Azure Security Center alert is created or triggered" is the correct choice. This Logic App acts as the workflow automation engine that runs whenever a new alert is raised. It can perform actions such as isolating VMs, disabling users, or notifying SOC teams.
Using a trigger for "When a response to an Azure Security Center alert is triggered" would only activate after a manual response, not automatically.
Automation runbooks with webhooks can be used for custom automation, but Defender workflow automation integrates natively with Logic Apps and not directly with runbooks.
# Final Answer:
Set available effects to: DeployIfNotExists
To perform remediation use: An Azure Logic Apps app that has the trigger set to When an Azure Security Center Alert is created or triggered
You have a Microsoft 365 subscription that uses Microsoft Defender XDR.
You are investigating an attacker that is known to use the Microsoft Graph API as an attack vector. The attacker performs the tactics shown the following table.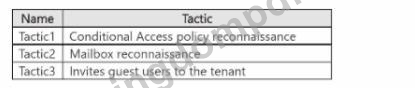
You need to search for malicious activities in your organization.
Which tactics can you analyze by using the MicrosoftGraphActivityLogs table?
- A. Tac1ic2 and Tactic3 only
- B. Tactic1 and Tactic2 only
- C. Tactic2 only
- D. Taclic1. Tac1ic2. andTactic3
Correct Answer: D 🗳️
Explanation: Only visible for CertkingdomPDF members. You can sign-up / login (it's free).
Viewing page 1 out of 83 pages.
Viewing questions 1-5 out of 415 questions.


 Rachel

 Hugh
 Penny

 Sharon
 Marico
 Jeffrey

 Riva
 Ingrid
 Hugh
 Ives
 Lennon
 Borg
 Victor
 Priscilla
 Afra


