


[2026] Use Valid New FCP_FCT_AD-7.4 Test Notes & FCP_FCT_AD-7.4 Valid Exam Guide
FCP_FCT_AD-7.4 Actual Questions Answers PDF 100% Cover Real Exam Questions
Fortinet FCP_FCT_AD-7.4 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 28
An administrator has lost web access to the FortiClient EMS console, and the web page to access to the console is timing out.
How can the administrator gather information to investigate the issue? (Choose one answer)
- A. Use the CLI diagnostic tool on the EMS server.
- B. Use the diagnostic logs option from the FortiClient EMS GUI.
- C. Download the webserver logs from the PostgreSQL server.
- D. Download the log generator from the support site and run it on the EMS server.
Answer: A
Explanation:
According to theFortiClient EMS Administrator Study Guideand officialTechnical Tipsfrom Fortinet, when the web console is inaccessible (e.g., timing out), the administrator must use tools available directly on the server's operating system (CLI) to gather diagnostic information.
1. Why the CLI Diagnostic Tool (Answer A) is the Correct Choice:
* Availability during Outage:When the GUI is unreachable, the standard "Generate Diagnostic Logs" option within the EMS interface is also unavailable.
* Windows-based EMS:The administrator can manually run the EMSDiagnosticTool.exe located at C:
\Program Files (x86)\Fortinet\FortiClientEMS\. This tool collects server information, Windows events, and EMS-specific logs into a compressed file for investigation.
* Linux-based EMS (v7.4+):For newer versions running on Linux, the administrator can use the CLI command: sudo /opt/forticlientems/bin/diagnostic_tool -o /tmp/diag to generate a diagnostic package.
* Service Verification:The CLI also allows administrators to verify if critical services (like fcems, apache2, or postgres) are running or if remote access has been disabled using the emscli utility.
2. Why Other Options are Incorrect:
* B. Download webserver logs from PostgreSQL:PostgreSQL is the database engine for EMS, not the web server. While database logs are useful, they are not the primary method for gathering general
"diagnostic information" and would typically be collected as part of the CLI diagnostic tool output rather than downloaded directly from the DB.
* C. Diagnostic logs option from the GUI:This option is impossible to use if the administrator has lost web access and the page is timing out.
* D. Download log generator from support site:While Fortinet provides various tools on their support site, theEMS Diagnostic Toolis natively installed with the FortiClient EMS software and is the primary, documented method for troubleshooting the EMS server itself.
NEW QUESTION # 29
Which security fabric component sends a notification to quarantine an endpoint after IOC detection in the automation process?
- A. FortiClient
- B. FortiAnalyzer
- C. D. Forti Gate
- D. ForbClient EMS
Answer: C
NEW QUESTION # 30
Refer to the exhibit.
Based on the settings shown in the exhibit which statement about FortiClient behavior is true?
- A. FortiClient blocks and deletes infected files after scanning them.
- B. FortiClient copies infected files to the Resources folder without scanning them.
- C. FortiClient scans infected files when the user copies files to the Resources folder
- D. FortiClient quarantines infected files and reviews later, after scanning them.
Answer: D
Explanation:
Action On Virus Discovery Warn the User If a Process Attempts to Access Infected Files Quarantine Infected Files. You can use FortiClient to view, restore, or delete the quarantined file, as well as view the virus name, submit the file to FortiGuard, and view logs. Deny Access to Infected Files Ignore Infected Files
NEW QUESTION # 31
Refer to the exhibit.
An administrator has restored the modified XML configuration file to FortiClient and sees the error shown in the exhibit.
Based on the XML settings shown in the exhibit, what must the administrator do to resolve the issue with the XML configuration file?
- A. The administrator must use a password to decrypt the file
- B. The administrator must resolve the XML syntax error.
- C. The administrator must change the file size
- D. The administrator must save the file as FortiClient-config conf.
Answer: B
Explanation:
Based on the error message and the XML configuration file shown in the exhibit:
* The error "Failed to process the file" typically indicates an issue with the XML syntax.
* Upon reviewing the XML content, it is crucial to ensure that all tags are correctly formatted, properly opened and closed, and that there are no syntax errors.
* Resolving any XML syntax errors will allow FortiClient to successfully process and restore the configuration file.
Therefore, the administrator must resolve the XML syntax error to fix the issue.
References
* FortiClient EMS 7.2 Study Guide, Configuration File Management Section
* General XML Syntax Guidelines and Best Practices
NEW QUESTION # 32
An administrator installs FortiClient EMS in the enterprise.
Which component is responsible for enforcing protection and checking security posture?
- A. FortiClient EMS tags
- B. FortiClient EMS
- C. FortiClient vulnerability scan
- D. FortiClient
Answer: D
Explanation:
* Understanding FortiClient EMS Components:
* FortiClient EMS manages and configures endpoint security settings, while FortiClient installed on the endpoint enforces protection and checks security posture.
* Evaluating Responsibilities:
* FortiClient performs the actual enforcement of security policies and checks the security posture of the endpoint.
* Conclusion:
* The component responsible for enforcing protection and checking security posture is FortiClient (C).
References:
FortiClient EMS and endpoint security documentation from the study guides.
NEW QUESTION # 33
ZTNA Network Topology
Refer to the exhibits, which show a network topology diagram of ZTNA proxy access and the ZTNA rule configuration.
An administrator runs the diagnose endpoint record list CLI command on FortiGate to check Remote-Client endpoint information, however Remote-Client is not showing up in the endpoint record list.
What is the cause of this issue?
- A. Remote-Client provided an invalid certificate to connect to the ZTNA access proxy.
- B. Remote-Client provided an empty client certificate to connect to the ZTNA access proxy.
- C. Remote-Client failed the client certificate authentication.
- D. Remote-Client has not initiated a connection to the ZTNA access proxy.
Answer: C
NEW QUESTION # 34
Which statement about FortiClient comprehensive endpoint protection is true?
- A. It helps to safeguard systems from data loss.
- B. lt helps to safeguard systems from advanced security threats, such as malware.
- C. It helps to safeguard systems from email spam
- D. It helps to safeguard systems from DDoS.
Answer: B
Explanation:
FortiClient provides comprehensive endpoint protection for your Windows-based, Mac-based, and Linuxbased desktops, laptops, file servers, and mobile devices such as iOS and Android. It helps you to safeguard your systems with advanced security technologies, all of which you can manage from a single management console.
NEW QUESTION # 35
An administrator has a requirement to add user authentication to the ZTNA access for remote or off-fabric users Which FortiGate feature is required m addition to ZTNA?
- A. FortiGate endpoint control
- B. FortiGate FSSO
- C. FortiGate certificates
- D. C. FortiGate explicit proxy
Answer: D
Explanation:
For adding user authentication to the ZTNA access for remote or off-fabric users, the following FortiGate feature is required in addition to ZTNA:
* FortiGate explicit proxyallows FortiGate to intercept web traffic for authentication purposes.
* ZTNA integrates with various FortiGate features to provide secure access and ensure that users are authenticated before accessing resources.
* By using an explicit proxy, FortiGate can handle web traffic and enforce authentication policies for remote users who are not directly on the corporate network (off-fabric).
Thus, the correct feature to use for this requirement is the FortiGate explicit proxy.
References
* FortiGate Security 7.2 Study Guide, ZTNA and Proxy Configuration Sections
* Fortinet Documentation on FortiGate Explicit Proxy and ZTNA Integration
NEW QUESTION # 36
Refer to the exhibit.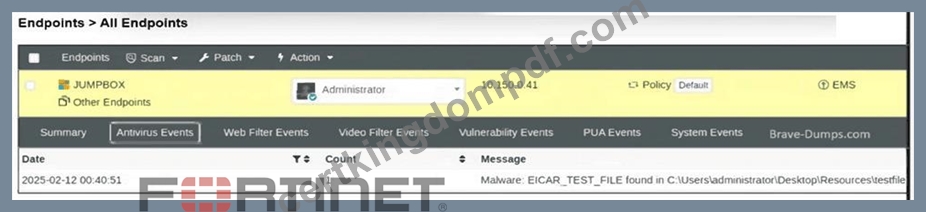
You provide a webserver hosting service. An endpoint downloads a test file, testfile.txt, that gets blocked by FortiClient.
Which configuration can you use to make the file accessible on the endpoint? (Choose one answer)
- A. Allow the webserver URL in the exclusion list in the web filter profile.
- B. Restore access to file directly using FortiClient.
- C. Add the file to the allowlist in quarantine management on FortiClient EMS.
- D. Exclude testfile.txt from the malware protection profile.
Answer: C
Explanation:
According to theFortiClient EMS 7.2/7.4 Administration Guide(specifically theQuarantine Management andMalware Protectionsections), the correct administrative workflow to restore a blocked file and ensure it is no longer flagged as malicious is to use theQuarantine Managementfeature on the EMS server.
1. Analysis of the Exhibit
* Event Type:The exhibit shows anAntivirus Eventwhere a file named testfile.txt was flagged as Malware: EICAR_TEST_FILE.
* Location:The file was found in a local user directory (C:
\Users\administrator\Desktop\Resources\testfile.txt).
* System State:The endpoint is managed by EMS (indicated by thePolicy: DefaultandEMSstatus icons).
2. Why Option D is the Correct Choice:
* Centralized Control:In a managed environment, the administrator uses the EMS console to oversee security incidents. To restore a file that has been quarantined, the administrator must navigate to Quarantine Management > Files.
* Allowlist & Restore Action:By selecting the specific blocked file (testfile.txt) and clickingAllowlist & Restore, two things happen simultaneously:
* Restoration:EMS sends a command to the FortiClient endpoint to release the file from the local quarantine folder and return it to its original path.
* Allowlisting:The file's hash is added to theAllowlist(managed underQuarantine Management > Allowlist), which prevents FortiClient from re-quarantining the file during future real-time or on- demand scans.
* Accessibility:This is the documented method to make a file "accessible on the endpoint" while ensuring it is not immediately re-blocked by the security engine.
3. Why Other Options are Incorrect:
* A. Restore access directly using FortiClient:While FortiClient has a local quarantine tab, the
"Release" button is typicallygreyed outor restricted when the client is managed by EMS to ensure centralized security policy enforcement.
* B. Allow the webserver URL in the exclusion list:The exhibit shows anAntivirus/Malwareevent, not aWeb Filterevent. The file has already been downloaded to the local disk and is being blocked by the Real-Time Protectionengine, so a Web Filter URL exclusion would have no effect on the local file block.
* C. Exclude testfile.txt from the malware protection profile:While adding a path exclusion to the Malware Protection profile is a valid way to prevent future scans of a directory, it doesnot automatically restorea file that hasalreadybeen moved to quarantine. The proper workflow for an existing block is to use the Quarantine Management tool first.
NEW QUESTION # 37
Refer to the exhibit, which shows FortiClient EMS deployment, profiles.
When an administrator creates a deployment profile on FortiClient EMS. which statement about the deployment profile is true?
- A. Deployment-2 will upgrade FortiClient on both the AD group and workgroup.
- B. Deployment-1 will install FortiClient on new AO group endpoints.
- C. Deployment-2 will install FortiClient on both the AD group and workgroup.
- D. Deployment-1 will upgrade FortiClient only on the workgroup.
Answer: A
Explanation:
* Deployment Profiles Analysis:
* Deployment-1 has the "First-Time-Installation" package and is assigned to "All Groups" with a priority of 1 but is not enabled.
* Deployment-2 has the "To-Upgrade" package, is assigned to both "All Groups" and "trainingAD.
training.lab," with a priority of 2 and is enabled.
* Evaluating Deployment-2:
* Deployment-2 will upgrade FortiClient on both "All Groups" and "trainingAD.training.lab" since it is enabled and assigned to these groups. This includes both AD (Active Directory) groups and workgroups.
* Conclusion:
* Since Deployment-2 is set to upgrade FortiClient on all the assigned groups and workgroups, the correct answer is A.
References:
FortiClient EMS deployment and profile documentation from the study guides.
NEW QUESTION # 38
Refer to the exhibit.
The zero trust network access (ZTNA) serial number on endpoint br-pc-1 is in a disabled state.
What is causing the problem? (Choose one answer)
- A. The ZTNA is disabled due to FortiClient disconnected from FortiClient EMS.
- B. The ZTNA feature is not installed on FortiClient.
- C. The ZTNA certificate has been revoked by administrator.
- D. The ZTNA destinations endpoint profile is disabled.
Answer: D
Explanation:
Based on theFortiClient EMS 7.2/7.4 Study Guidesand the visual evidence provided in the exhibit, here is the verified breakdown of why theZTNA Serial Numberis showing asDisabled:
1. Analysis of the Exhibit
* Operating System:The endpoint is runningLinux (Ubuntu 22.04.3 LTS).
* Connection Status:The endpoint status isOnlineandManaged by EMS. This immediately eliminates Option C, as the device is actively communicating with the EMS server.
* Features List:At the bottom right of the "Features" column, it explicitly states"ZTNA installed". This eliminatesOption A, confirming the software component is present on the endpoint.
* ZTNA Serial Number Field:The field is highlighted in red and shows"Disabled".
2. Identifying the Root Cause (Option B)
In the FortiClient EMS curriculum regardingZTNA (Zero Trust Network Access), the ZTNA Serial Number (also known as the ZTNA Tagging or Client Certificate UID) is generated and activated based on the assigned Endpoint Profile.
* Profile Dependency:For FortiClient to generate a ZTNA serial number/certificate and participate in ZTNA, the administrator must enable and configure theZTNA Destinations(or ZTNA Connection) profile within the EMS.
* Disabled State:If theZTNA Destinationsfeature is disabled in the profile assigned to that specific endpoint (or if the endpoint is assigned the "Default" profile where ZTNA is not configured), the
"ZTNA Serial Number" status on the EMS dashboard will reflect asDisabled.
* Linux Specifics:In FortiClient for Linux, ZTNA support is available but requires the profile to be explicitly pushed and active. If the profile is toggled off in the EMS GUI underEndpoint Profiles > ZTNA Destinations, the serial number functionality is suspended.
3. Why Other Options are Incorrect
* A. The ZTNA feature is not installed:The exhibit clearly shows "ZTNA installed" under the Features list.
* C. FortiClient disconnected from EMS:The exhibit shows the status as "Online" and "Managed by EMS" with a green checkmark.
* D. The ZTNA certificate has been revoked:If a certificate is revoked, the status typically shows as
"Revoked" or "Expired," or the serial number would still be present but marked as untrusted. A
"Disabled" state indicates the feature itself is turned off at the policy/profile level.
NEW QUESTION # 39
What is the function of the quick scan option on FortiClient?
- A. It scans executable files. DLLs, and drivers that are currently running, for threats.
- B. It allows users to select a specific file folder on their local hard disk drive (HDD), to scan for threats.
- C. It scans programs and drivers that are currently running, for threats
- D. It performs a full system scan including all files, executable files. DLLs, and drivers for throats.
Answer: D
Explanation:
* Understanding Quick Scan Function:
* The quick scan option on FortiClient is designed to scan certain elements of the system quickly for threats.
* Evaluating Scan Scope:
* The quick scan specifically targets executable files, DLLs, and drivers that are currently running, providing a rapid assessment of the active components of the system.
* Conclusion:
* The correct answer is D, as it accurately describes the function of the quick scan option on FortiClient.
References:
FortiClient scanning options documentation from the study guides.
NEW QUESTION # 40
An administrator configures ZTNA configuration on the FortiGate. Which statement is true about the firewall policy?
- A. It defines ZTNA server.
- B. It only uses ZTNA tags to control access for endpoints.
- C. It redirects the client request to the access proxy.
- D. It uses the access proxy.
Answer: C
Explanation:
"The firewall policy matches and redirects client requests to the access proxy VIP"https://docs.fortinet.com
/document/fortigate/7.0.0/new-features/194961/basic-ztna-configuration
NEW QUESTION # 41
An administrator is required to maintain a software vulnerability on the endpoints, without showing the feature on the FortiClient. What must the administrator do to achieve this requirement?
- A. Disable select the vulnerability scan feature in the deployment package
- B. Use the default endpoint profile
- C. Click the hide icon on the vulnerability scan profile assigned to endpoint
- D. Select the vulnerability scan feature in the deployment package, but disable the feature on the endpoint profile
Answer: C
Explanation:
* Requirement Analysis:
* The administrator needs to maintain a software vulnerability scan on endpoints without showing the feature on FortiClient.
* Evaluating Options:
* Disabling the feature in the deployment package or endpoint profile would remove the functionality entirely, which is not desired.
* Using the default endpoint profile may not meet the specific requirement of hiding the feature.
* Clicking the hide icon on the vulnerability scan profile assigned to the endpoint will keep the feature active but hidden from the user's view.
* Conclusion:
* The correct action is to click the hide icon on the vulnerability scan profile assigned to the endpoint (C).
References:
FortiClient EMS feature configuration and management documentation from the study guides.
NEW QUESTION # 42
When multitenancy is enabled on FortiClient EMS, which administrator role can provide access to the global site only? (Choose one answer)
- A. Tenant administrator
- B. Global administrator
- C. Standard administrator
- D. Settings administrator
Answer: D
Explanation:
According to theFortiClient EMS Administration Guide(specifically the sections onMultitenancy), when multitenancy is enabled, the system introduces specific administrator roles to manage the separation between global settings and individual sites.
1. The Settings Administrator Role (Answer B)
* Specific Scope:TheSettings administratoris a specialized role designed to haveaccess to the global site only.
* Permissions:This role can access all configuration options on the global site, with the notable exception ofadministrator configuration(they cannot create or manage other admin accounts).
* Use Case:This is typically used for auditors or system managers who need to oversee global-level configurations without needing access to specific endpoint data within individual sites or the power to modify administrative users.
2. Comparison with Other Multitenancy Roles
* Super administrator:This role hasunlimited accessto the global site andall other siteswithin the EMS instance.
* Site administrator:This role is restricted tospecified sites onlyand hasno access to the global site.
* Standard administrator (Answer C):This is a generic role level within a site or a single-tenant environment but is not the role that defines "global-only" access in a multitenant setup.
* Tenant administrator / Global administrator:While these terms are common in general IT, FortiClient EMS documentation specifically uses the titlesSuper,Settings, andSiteadministrators for multitenancy management.
3. Curriculum References
* FortiClient EMS 7.2/7.4 Study Guide (Multitenancy Chapter):Explicitly lists "Settings administrator" as the role providing access to the global site only.
* Admin Roles Table:The documentation provides a comparison table where the Settings Administrator's scope is strictly defined as "Global site only".
NEW QUESTION # 43
Refer to the exhibits.

Which show the Zero Trust Tag Monitor and the FortiClient GUI status.
Remote-Client is tagged as Remote-Users on the FortiClient EMS Zero Trust Tag Monitor.
What must an administrator do to show the tag on the FortiClient GUI?
- A. Change the user identity settings to enable tag visibility
- B. B. Change the FortiClient system settings to enable tag visibility
- C. Change the endpoint control setting to enable tag visibility
- D. Update tagging rule logic to enable tag visibility
Answer: B
Explanation:
Based on the exhibits provided:
* The "Remote-Client" is tagged as "Remote-Users" in the FortiClient EMS Zero Trust Tag Monitor.
* To ensure that the tag "Remote-Users" is visible in the FortiClient GUI, the system settings within FortiClient need to be updated to enable tag visibility.
* The tag visibility feature is controlled by FortiClient system settings which manage how tags are displayed in the GUI.
Therefore, the administrator needs to change the FortiClient system settings to enable tag visibility.
References
* FortiClient EMS 7.2 Study Guide, Zero Trust Tagging Section
* FortiClient Documentation on Tag Management and Visibility Settings
NEW QUESTION # 44
Which two statements apply to FortiClient forensics analysis? (Choose two answers)
- A. Forensics analysis features must be enabled in the system settings profile.
- B. FortiClient sends an alert notification when malicious activity is triggered.
- C. The endpoint is quarantined until forensics is completed.
- D. The administrator must request analysis for the desired endpoint.
Answer: A,D
Explanation:
Based on theFortiClient EMS 7.2/7.4 Administrator Study Guideand theFortiGuard Forensics Service User Guide, the forensics analysis feature is a specialized service that requires specific administrative actions and configuration.
1. The Administrator Must Request Analysis (Answer B)
* Manual Initiation: Unlike standard Antivirus or Sandbox scans which occur automatically upon detection, theFortiGuard Forensics Analysisis a service-based investigation.
* Workflow: Once a threat is detected or a device is suspected of being compromised, the administrator must navigate to theEndpointspane, select the specific device, and click theRequest Analysisbutton.
* Escalation: The administrator then fills out a questionnaire (providing the reason for escalation and issue summary) to submit the logs to the FortiGuard Labs forensic team for manual review.
2. Forensics Features Must be Enabled in the Profile (Answer D)
* Two-Step Enabling:
* Global Level: First, the feature must be toggled on underSystem Settings > Feature Select > FortiGuard Forensics Analysis.
* Profile Level: Crucially, it must be enabled within theEndpoint Profile(specifically under System Settings) that is applied to the target endpoints.
* Agent Deployment: Toggling this in the profile ensures the FortiClient endpoint prepares the
"forensics agent" components required to collect deep-system data (such as the Master File Table, Windows Event Logs, and registry hives) when a request is eventually made.
3. Why Other Options are Incorrect
* A. FortiClient sends an alert notification: While FortiClient does send alerts for malicious activity, this is part of the standardEndpoint ControlandMalware Protectionmodules. Theforensics analysis itself is the follow-up investigation performed after such an alert is received and reviewed by an admin.
* C. The endpoint is quarantined until completed: Although it is a security "Best Practice" to quarantine a compromised endpoint during an investigation, the forensics analysis process does not programmatically force or require a quarantine state to function. The forensics agent can collect logs from an online, non-quarantined device as long as it has EMS connectivity.
NEW QUESTION # 45
Why does FortiGate need the root CA certificate of FortiCient EMS?
- A. To trust certificates issued by FortiClient EMS
- B. To sign FortiClient CSR requests
- C. To revoke FortiClient client certificates
- D. To update FortiClient client certificates
Answer: C
Explanation:
* Understanding the Need for Root CA Certificate:
* The root CA certificate of FortiClient EMS is necessary for FortiGate to trust certificates issued by FortiClient EMS.
* Evaluating Use Cases:
* FortiGate needs the root CA certificate to establish trust and validate certificates issued by FortiClient EMS.
* Conclusion:
* The primary reason FortiGate needs the root CA certificate of FortiClient EMS is to trust certificates issued by FortiClient EMS.
References:
FortiClient EMS and FortiGate certificate management documentation from the study guides.
NEW QUESTION # 46
Which Fortinet solution can you integrate FortiClient with to use the single sign-on mobility agent (SSOMA) feature? (Choose one answer)
- A. FortiAuthenticator
- B. FortiNAC
- C. FortiSASE
- D. FortiPAM
Answer: A
Explanation:
According to theFortiClient EMS 7.2/7.4 Administration GuideandFortiAuthenticator Study Guides, the Single Sign-On Mobility Agent (SSOMA)is a feature specifically designed to integrate with FortiAuthenticatorto provide transparent, identity-based authentication.
1. Integration with FortiAuthenticator (Answer A)
* The SSOMA Service:The mobility agent service is hosted on theFortiAuthenticatorunit.
Administrators must navigate toFortinet SSO Methods > SSO > Generalon the FortiAuthenticator and toggle onEnable FortiClient SSO Mobility Agent Service.
* Communication Protocol:FortiClient communicates with FortiAuthenticator via a specified TCP listening port (defaulting to8001or8005) and uses apre-shared key(secret key) for authentication.
* Transparent Authentication:Once configured, the SSOMA on the endpoint automatically sends user logon information and IP address changes (such as WiFi roaming) to FortiAuthenticator.
FortiAuthenticator then shares this information with FortiGate units to enforce identity-based security policies without the user needing to re-authenticate manually.
2. Modern Capabilities (Azure AD / Entra ID)
* Cloud Integration:In FortiClient 7.2.1 and later, SSOMA supportsnative Azure AD (Entra ID). In this mode, the agent sends the Azure AD domain and tenant ID directly to FortiAuthenticator, allowing organizations to create identity-based policies for cloud-joined devices.
3. Note on FortiPAM (Option C)
* Recent Updates:While recent FortiClient EMS 7.4 documentation mentions an"Add FortiPAM agent to SSOMA"feature, this is an extension of the existing SSOMA framework. The core product that defines and runs the SSOMA service for general Single Sign-On (SSO) remainsFortiAuthenticator.
4. Why Other Options are Incorrect
* B. FortiSASE:While FortiSASE uses FortiClient for Secure Internet Access (SIA), it uses different mechanisms (like SAML or the SASE cloud portal) for user identity rather than the specific SSOMA agent service.
* D. FortiNAC:FortiNAC uses FortiClient for persistent agent-based posture assessment and scanning, but it does not utilize the SSOMA mobility agent for user-to-IP mapping.
NEW QUESTION # 47
Which security attribute is verified during the SSL connection negotiation between FortiClient and FortiClient EMS to mitigate man-in-the-middle (MITM) attacks? (Choose one answer)
- A. organization (O)
- B. common name (CN)
- C. location (L)
- D. serial number (SN)
Answer: B
Explanation:
According to theFortiClient EMS Administrator Study Guide (7.2/7.4 versions)and theFortinet Document LibraryregardingSSL/TLS Endpoint Communication Security, the primary attribute verified during the SSL connection negotiation to mitigate Man-in-the-Middle (MITM) attacks is theCommon Name (CN).
1. SSL Connection Negotiation & MITM Mitigation
* Verification Process: When FortiClient attempts to establish aTelemetry connectionwith the FortiClient EMS server, an SSL handshake occurs. To ensure it is communicating with the legitimate server and not a malicious interceptor (MITM), FortiClient verifies the server's certificate.
* Role of the Common Name (CN): TheCommon Name(or theSubject Alternative Name - SAN) in the certificate must match theFQDN (Fully Qualified Domain Name)or theIP addressthat the client intended to connect to.
* Security Enforcement: If the CN/SAN does not match the server's expected address, FortiClient will detect a discrepancy. Depending on theInvalid Certificate Actionsetting in the profile (e.g., Warn or Block), it will prevent the establishment of a secure session to stop the MITM attacker from masquerading as the EMS server.
2. Why Other Options are Incorrect/Secondary
* A. Serial Number (SN): While every certificate has a unique Serial Number, it is primarily used by the Certificate Authority (CA) for tracking and revocation purposes. While FortiOS 7.2.4+ can use SN for certain restricted VPN checks, the core SSL negotiation mechanism for identifying a specific host to prevent spoofing relies on theCN/SANfields.
* C. Location (L) and D. Organization (O): These are descriptive fields within the certificate'sSubject that provide geographical and corporate information. They are not functionally used by the SSL/TLS protocol to verify the identity of the host during the connection negotiation or to mitigate MITM attacks.
3. Curriculum References
* EMS Administration Guide (System Settings Profile): Details how the client verifies the EMS server certificate. It specifies that for a connection to be trusted, the server address must align with the certificate's identity fields (CN/SAN).
* FortiGate/FortiOS 7.2.4 New Features: Highlights the specific enhancement where FortiClient EMS connectors now "trust EMS server certificate renewals based on theCN field" to ensure continuous secure communication.
NEW QUESTION # 48
Which statement about FortiClient enterprise management server is true?
- A. It provides centralized management of FortiGate devices.
- B. It provides centralized management of FortiClient Android endpoints only.
- C. lt provides centralized management of multiple endpoints running FortiClient software.
- D. It provides centralized management of Chromebooks running real-time protection
Answer: C
Explanation:
FortiClient EMS is designed to provide centralized management and control of multiple endpoints running FortiClient software. It serves as a central management server that allows administrators to efficiently manage and configure a large number of FortiClient installations across the network.
NEW QUESTION # 49
Which two statements are true about the ZTNA rule? (Choose two.)
- A. It applies security profiles to protect traffic
- B. It applies SNAT to protect traffic.
- C. It enforces access control.
- D. It defines the access proxy.
Answer: A,C
Explanation:
* Understanding ZTNA Rule Configuration:
* The ZTNA rule configuration shown in the exhibit defines how traffic is managed and controlled based on specific tags and conditions.
* Evaluating Rule Components:
* The rule includes security profiles to protect traffic by applying various security checks (A).
* The rule also enforces access control by determining which endpoints can access the specified resources based on the ZTNA tag (D).
* Eliminating Incorrect Options:
* SNAT (Source Network Address Translation) is not mentioned as part of this ZTNA rule.
* The rule does not define the access proxy but uses it to enforce access control.
* Conclusion:
* The correct statements about the ZTNA rule are that it applies security profiles to protect traffic (A) and enforces access control (D).
References:
ZTNA rule configuration documentation from the study guides.
NEW QUESTION # 50
Which two are benefits of using multi-tenancy mode on FortiClient EMS? (Choose two.)
- A. The fabric connector must use an IP address to connect to FortiClient EMS.
- B. Separate host servers manage each site.
- C. Licenses are shared among sites
- D. It provides granular access and segmentation.
Answer: A,D
Explanation:
* Understanding Multi-Tenancy Mode:
* Multi-tenancy mode allows multiple independent sites or tenants to be managed from a single FortiClient EMS instance.
* Evaluating Benefits:
* Licenses can be shared among sites, making it cost-effective (B).
* It provides granular access and segmentation, allowing for detailed control and separation between tenants (D).
* Eliminating Incorrect Options:
* Separate host servers managing each site (A) is not a feature of multi-tenancy mode.
* The fabric connector's use of an IP address (C) is unrelated to multi-tenancy benefits.
References:
FortiClient EMS multi-tenancy configuration and benefits documentation from the study guides.
NEW QUESTION # 51
......
FCP_FCT_AD-7.4 Exam questions and answers: https://torrentvce.certkingdompdf.com/FCP_FCT_AD-7.4-latest-certkingdom-dumps.html